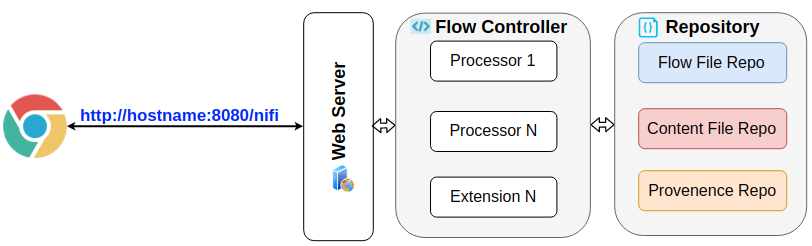
Default Apache Nifi installation comes without security layer which exposes the development UI. As a result, users can freely access the Nifi project development with knowledge about the hostname and binding Port. You can see two potential security risks: * **Flow controller attack** : full policies to modify the processor on Flow Controller. * **API attack**: external invoked requests to start/stop/delete Nifi components. ## Implement strategy To protect the unexpected security issues related, this post will help to list out steps by steps to setup security layer in the default Apache Nifi installation. The LDAP User Authentication method is used because of its easy to manage and setup while maintains secured manner. Details on can be found [HERE](https://nifi.apache.org/docs/nifi-docs/html/administration-guide.html#ldap_login_identity_provider) from the official website. There are three main components added to the previously diagram, including LDAP server, Authentication and Authentization: * **LDAP server**: manage the users’ access to Nifi server. This server can be deployed within same or seperate server with Nifi. In this post, the OpenLDAP library is used as its popularity. * **Authentication**: enable authentication feature to perform a handshake with LDAP server to recognize who is logging on the server. * **Authorization**: distinguish the which policies are applied for current login account. To enable these 3 components, it required to setup an additional LDAP server apart from Nifi service; and perform configuration for number of config files such as nifi.properties, login-identity-providers.xml, authorizers.xml, etc. The next 3 sections will describe the implementation details for these 3 componenents. 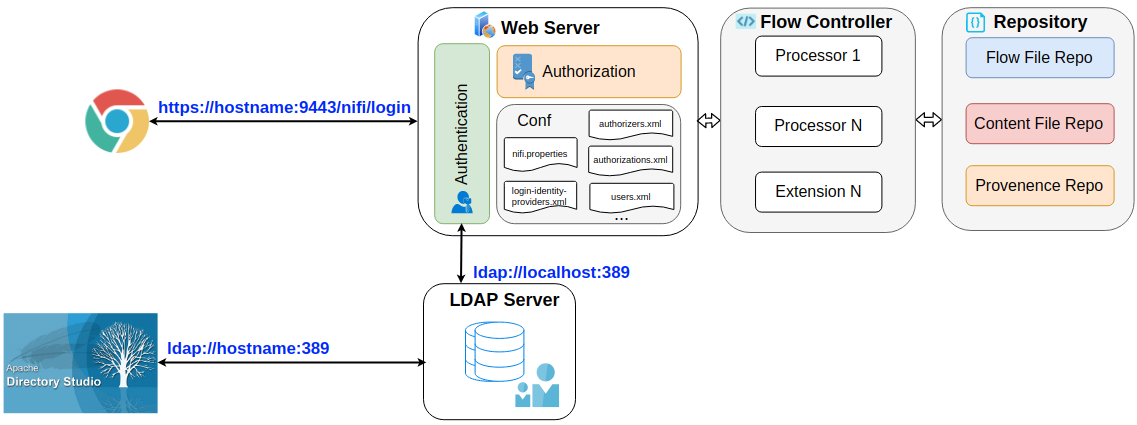 ## LDAP Server Simply run an OpenLDAP docker as below: ```bash docker run --name vanducng-openldap --env LDAP_ORGANISATION="myorg" --env LDAP_DOMAIN="vanducng.dev" --env LDAP_ADMIN_PASSWORD="SuperSecret" -p 389:389 -p 636:636 -d osixia/openldap ``` We target run on domain vanducng.dev with initial admin password of “SuperSecret” which later on can be change via ADS. Further configurations can be found from [here](https://github.com/osixia/docker-openldap). ## Authentication Then LDAP server is now accessible using docker machine IP. It can be checked by `iptables -L` command: However, to enable a handshake with LDAP server, Nifi has to be configured to enable HTTPS/SSL first as stated in the [official document](https://nifi.apache.org/docs/nifi-docs/html/administration-guide.html#user_authentication). ### Use toolkit to generate config files Start following commands to download the nifi toolkit to generate the List of configuration files are shown as below including keystore.jks, nifi-cert.pem, nifi-key.key, nifi.properties, truststore.jks. ```bash wget http://www-eu.apache.org/dist/nifi/1.10.0/nifi-toolkit-1.10.0-bin.tar.gz tar xvf nifi-toolkit-1.10.0-bin.tar.gz cd nifi-toolkit-1.10.0/bin ./tls-toolkit.sh standalone -n 'vanducng.dev' mv nifi-* vanducng.dev/ ``` Move these files to conf folder under nifi location: ```bash mv vanducng.dev/* /nifi/conf/ ``` ### Edit nifi.properties Open the file with preferred text editor: ```bash nano /nifi/conf/nifi.properties ``` In web properties section, apply the https hostname and specific port as following. The hostname must be same as domain name for public access, else the webserver will return a header error. In this example, I was using Amazon EC2 as remote server. ```perl nifi.properties # web properties # nifi.web.war.directory=./lib nifi.web.http.host= nifi.web.http.port= nifi.web.http.network.interface.default= nifi.web.https.host=ec2-xxx-xxx-xxx-xxx.ap-southeast-1.compute.amazonaws.com nifi.web.https.port=9443 nifi.web.https.network.interface.default= nifi.web.jetty.working.directory=./work/jetty nifi.web.jetty.threads=200 nifi.web.max.header.size=16 KB nifi.web.proxy.context.path= nifi.web.proxy.host= ``` Ensure the ldap-provider is configured in `nifi.security.user.login.identity.provider` as well. ```perl nifi.properties # security properties # nifi.sensitive.props.key= nifi.sensitive.props.key.protected= nifi.sensitive.props.algorithm=PBEWITHMD5AND256BITAES-CBC-OPENSSL nifi.sensitive.props.provider=BC nifi.sensitive.props.additional.keys= nifi.security.keystore=./conf/keystore.jks nifi.security.keystoreType=jks nifi.security.keystorePasswd=OYW1Iuvk1Wi1Oraccw7/wTdHn1GzeWI5btS+7vPB8tc nifi.security.keyPasswd=OYW1Iuvk1Wi1Oraccw7/wTdHn1GzeWI5btS+7vPB8tc nifi.security.truststore=./conf/truststore.jks nifi.security.truststoreType=jks nifi.security.truststorePasswd=uTxsOQauQ3a7PopBfVjHGn7+UqWXG2Gn8j4sDax6ykA nifi.security.user.authorizer=managed-authorizer nifi.security.user.login.identity.provider=ldap-provider nifi.security.ocsp.responder.url= nifi.security.ocsp.responder.certificate= ``` ### Map hostname with private IP address Open hosts file: ```bash nano /etc/hosts ``` Map the private IP address of the EC2 instance with the hostname defined in nifi.properties config file. ```bash 172.31.23.12 ec2-xxx-xxx-xxx-xxx.ap-southeast-1.compute.amazonaws.com ``` ### Edit login-identity-providers.xml Similar to nifi.properties, open login-identity-providers.xml with preferred text editor, then uncomment ldap-provider xml block and configure the LDAP information that has been setup in previous step. ```xml login-identity-providers.xml